Yes — Lufkin accounting firm Todd, Hamaker & Johnson, LLP (cpaonpoint.com) was listed by the Akira ransomware group in late June 2026, and the firm later confirmed the intrusion at a Hudson City Council meeting, according to the Lufkin Daily News.
Akira claimed roughly 40 GB of company and client data — financial records, contracts, SSNs, driver’s licenses, and passports — and threatened public release. CPA firms routinely hold tax returns, payroll, and identity documents, so a confirmed listing is a client identity-theft and follow-on phishing event as much as an IT outage.
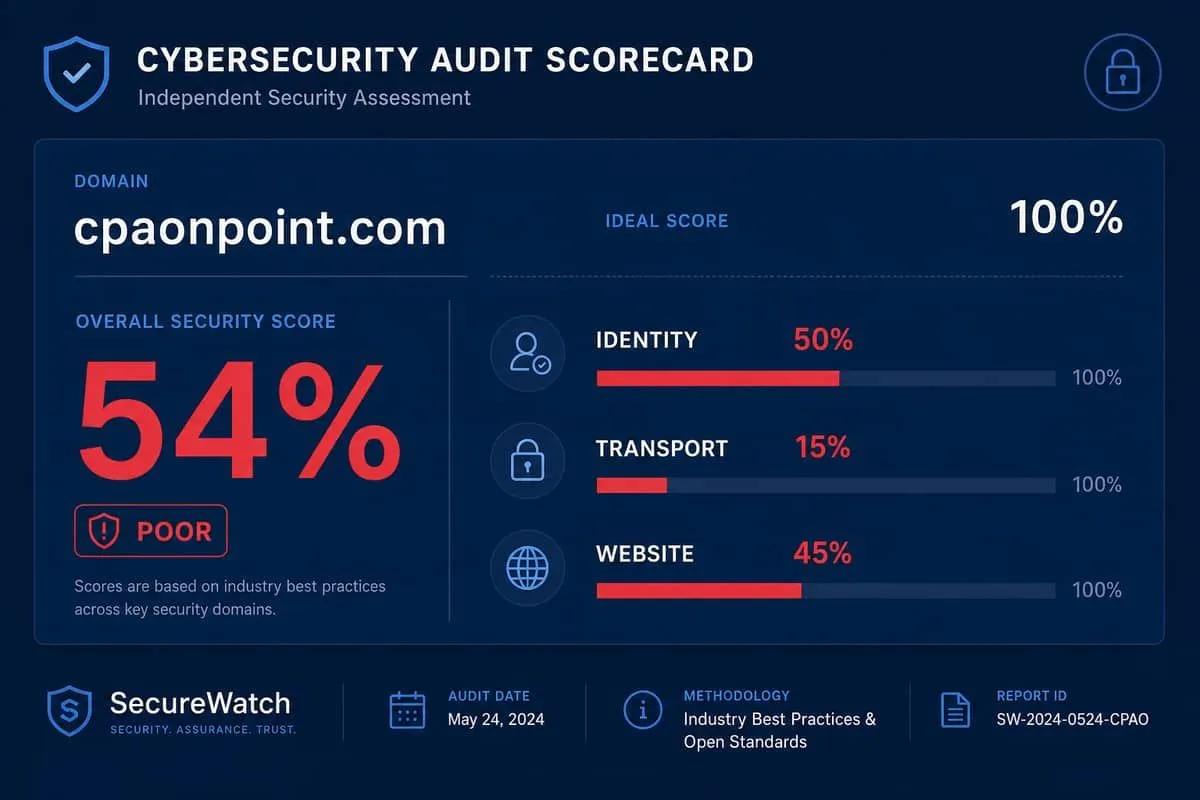
We scanned cpaonpoint.com against a 100% ideal domain-security score.
What Happened
According to the Lufkin Daily News listing report and the firm’s later public confirmation:
- Late June 2026 — Akira listed Todd, Hamaker & Johnson on its dark-web leak site (~40 GB claimed).
- SOCRadar, DeXpose, and BreachSense independently documented the listing.
- July 2026 (Hudson City Council) — Partner Kim Johnson confirmed a multi-week “computer incident,” saying attackers accessed two server drives, stole/encrypted roughly 55,000 files, wiped network systems, and forced the firm offline for several days while attorneys, negotiators, and cybersecurity specialists responded.
- Johnson said tax and audit software were not compromised, but forensic “data mining” was still required before notifying specific clients — a delay Hudson Mayor Caleb Ramsey criticized as leaving people without early credit-monitoring options.
Akira routinely uses double extortion: steal data first, encrypt second, then threaten public release.
Incident at a Glance
| Field | Detail |
|---|---|
| Entity | Todd, Hamaker & Johnson, LLP |
| Domain | cpaonpoint.com |
| Sector | CPA / tax & audit (Lufkin & Crockett, Texas) |
| Threat actor | Akira |
| Listing window | Late June 2026 |
| Claimed volume | ~40 GB / ~55,000 files |
| Org confirmation | Yes (Hudson City Council) |
| Data types claimed | Financials, contracts, SSNs, IDs, passports, audit working papers |
Data at Risk
| Category | Why it matters |
|---|---|
| Client financial records & contracts | Tax-refund fraud, vendor impersonation |
| SSNs, driver’s licenses, passports | Identity theft and new-account fraud |
| Employee files | Payroll and benefits fraud |
| Temporary audit server exports | Client PII in working papers |
Regulatory Context
| Requirement | Why it matters here |
|---|---|
| Texas Business & Commerce Code §521.053 | Notify AG when a breach affects 250+ Texas residents — as soon as practicable, not later than 30 days after determination |
| CPA confidentiality / client trust | Tax and audit data are among the most sensitive records mid-market firms hold |
| SB 2610 framing | Documented cybersecurity safeguards matter when Texans’ personal data is at stake |
Why Texas CPA Firms Should Care
Regional accounting firms are high-value ransomware targets: flat networks, shared temporary audit shares, and Microsoft 365 mail that looks “enterprise” while DMARC / MTA-STS still score far below 100%. Post-listing windows drive fake “credit monitoring” and “tax transcript” phishing against @cpaonpoint.com lookalikes.
Related East Texas healthcare listing: East Texas Family Medicine / Genesis.
Independent Cybersecurity Audit
We ran an EmailMeNow Cybersecurity Audit of cpaonpoint.com on July 11, 2026. 100% is the ideal overall score for organizations handling tax IDs and client SSNs.
Scorecard (Ideal = 100%)
| Domain | Overall | Identity | Transport | Website | Email infra | Risk |
|---|---|---|---|---|---|---|
| Ideal posture | 100% | 100% | 100% | 100% | Enterprise M365/Google | — |
| cpaonpoint.com | 54% | 50% | 15% | 45% | 100% (Microsoft 365) | Critical |
Gap vs Ideal
| Control area | Ideal | Score | Gap |
|---|---|---|---|
| Overall | 100% | 54% | −46 |
| Identity & Spoofing | 100% | 50% | −50 |
| Transport Security | 100% | 15% | −85 |
| Website Security | 100% | 45% | −55 |
Key findings:
- 54% overall (Critical Risk) — roughly halfway below the 100% ideal for a CPA firm handling SSNs and tax correspondence.
- 50% Identity & Spoofing — incomplete DMARC/SPF enforcement leaves room for spoofed partner and client emails during an active notification window.
- 15% Transport Security — no effective MTA-STS
mode=enforceor TLS-RPT reporting. - 100% Email Infrastructure — Microsoft 365 / Exchange is solid hosting but does not offset weak identity and transport scores.
- 45% Website Security — public web hardening lags.
Weak public-domain email controls do not cause ransomware by themselves, but they amplify harm when attackers already claim client contact data.
Audit link: cpaonpoint.com audit
Priority Actions
If you are a Todd, Hamaker & Johnson client:
- Treat unsolicited “breach help” or tax-transcript texts/emails as hostile until you verify through a known phone number.
- Use IdentityTheft.gov for fraud alerts or credit freezes.
- Watch for fraudulent tax filings opened in your name.
For Texas CPA and professional-service firms:
- Enforce phishing-resistant MFA on Microsoft 365, tax software, VPN, and backup admin accounts.
- Deploy DMARC
p=reject(with aligned SPF/DKIM) on every client-facing domain. - Add MTA-STS
mode=enforceand TLS-RPT to close the −85 transport gap. - Segment temporary audit/export shares from backup and identity systems.
- Pre-write notification playbooks so forensic delay does not become the only public story.
Related Trackers
- East Texas Family Medicine Genesis ransomware
- Ransomware threat landscape
- Texas OAG YTD dashboard
- Breach monitoring guide
Protect client tax data and East Texas business email.
Check your domain free at audit.emailmenow.com, or see automated reports and monitoring.
Sources: Lufkin Daily News — Lufkin accounting firm listed by Akira · Lufkin Daily News — Todd, Hamaker & Johnson confirms ransomware attack · Todd, Hamaker & Johnson — cpaonpoint.com · EmailMeNow audit — cpaonpoint.com
SB 2610 may help limit exemplary damages for eligible businesses that maintain a documented cybersecurity program; not legal advice or a guarantee.