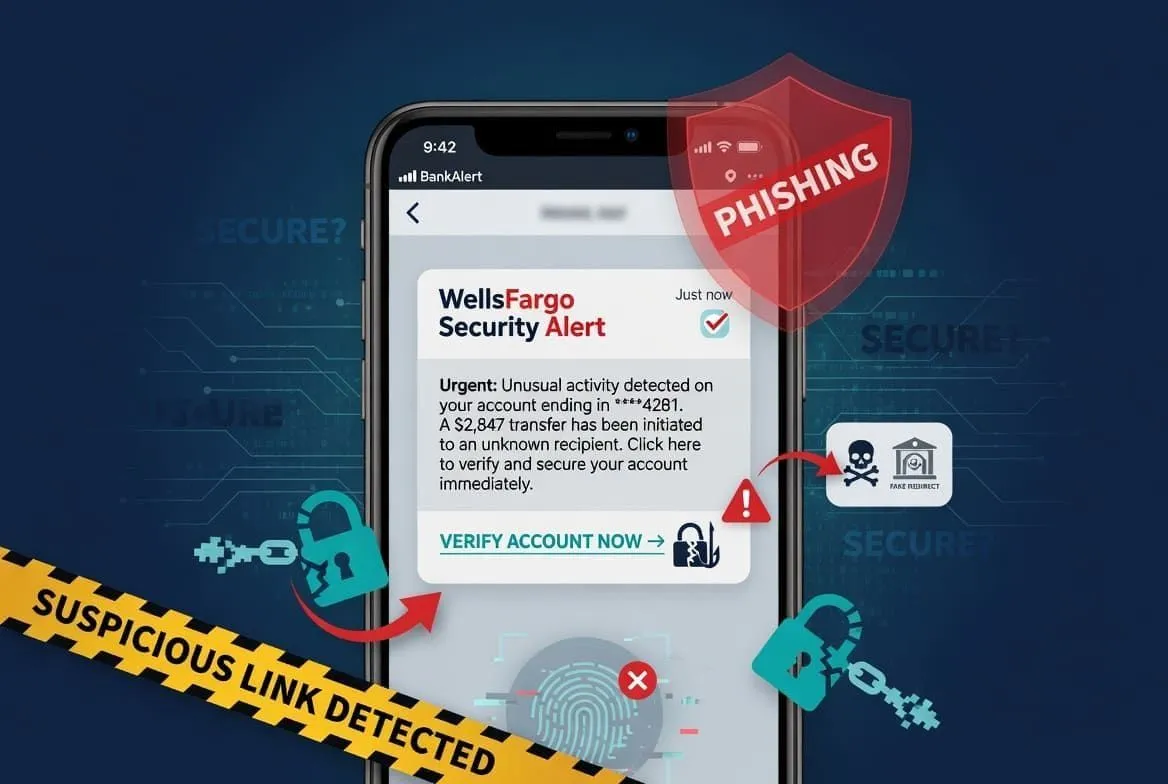
According to PropertyCasualty360, a sophisticated text message scam has led to more than $300,000 being stolen from bank accounts.
The attacks, known as smishing (SMS phishing), involve fraudsters sending deceptive text messages that appear to come from legitimate banks or financial institutions. Victims are tricked into clicking malicious links or providing sensitive information, allowing criminals to drain funds from their accounts.
What Happened
Scammers are using increasingly convincing tactics, including:
- Fake alerts about suspicious account activity
- Urgent messages claiming accounts will be locked
- Requests to “verify” identity through fake login pages
These attacks have become more targeted and professional in appearance, making them harder for individuals to detect.
Why This Matters for Law Firms
Law firms are particularly attractive targets because they often manage large sums of client funds in trust accounts. A successful attack could result in:
- Significant financial losses
- Potential professional responsibility concerns under Texas disciplinary rules
- Damage to client trust and firm reputation
With the rise of remote work and mobile banking, attorneys and staff are increasingly vulnerable to these types of attacks.
Key Protection Recommendations
- Never click links in unsolicited text messages from banks
- Always verify by logging in directly through the official bank app or website
- Enable transaction alerts and monitor accounts daily
- Train staff regularly on recognizing smishing and phishing attempts
- Use multi-factor authentication on all financial and email accounts
Check your domain free at audit.emailmenow.com or see automated reports and monitoring.