3 New California AG Breach Notices Published September 4, 2026
California's data breach list added 3 notices on September 4, 2026. California does not publish residents-affected counts — this roundup tracks reporting visibility.
Read UpdateNews
Page 5 of 31 — 923 updates. Back to latest · By industry · National audits
Instant audit
Run a free scan at audit.emailmenow.com, then unlock the Full Audit Report with Fix Kit steps and compliance evidence for $99.
California's data breach list added 3 notices on September 4, 2026. California does not publish residents-affected counts — this roundup tracks reporting visibility.
Read Update
HHS OCR listed 2 large HIPAA breach submissions dated September 4, 2026, affecting 1,990 individuals nationally. Minuteman Press Macon led the batch with 1,489 individuals.
Read Update
Texas OAG published 4 new data security breach reports on September 4, 2026, affecting 22,252 Texans. LHC Group, Inc led the batch with 16,885 affected.
Read Update
Washington's Attorney General published 3 new data breach notifications on September 4, 2026, affecting 11,403 Washingtonians. LHC Group, Inc. led the batch with 6,602 affected.
Read Update
California's data breach list added 6 notices on September 2, 2026. California does not publish residents-affected counts — this roundup tracks reporting visibility.
Read Update
Have I Been Pwned added 1 breach on September 2, 2026, exposing 8,849,657 accounts globally. Manchester Airports Group led the batch with 8,849,657 accounts.
Read Update
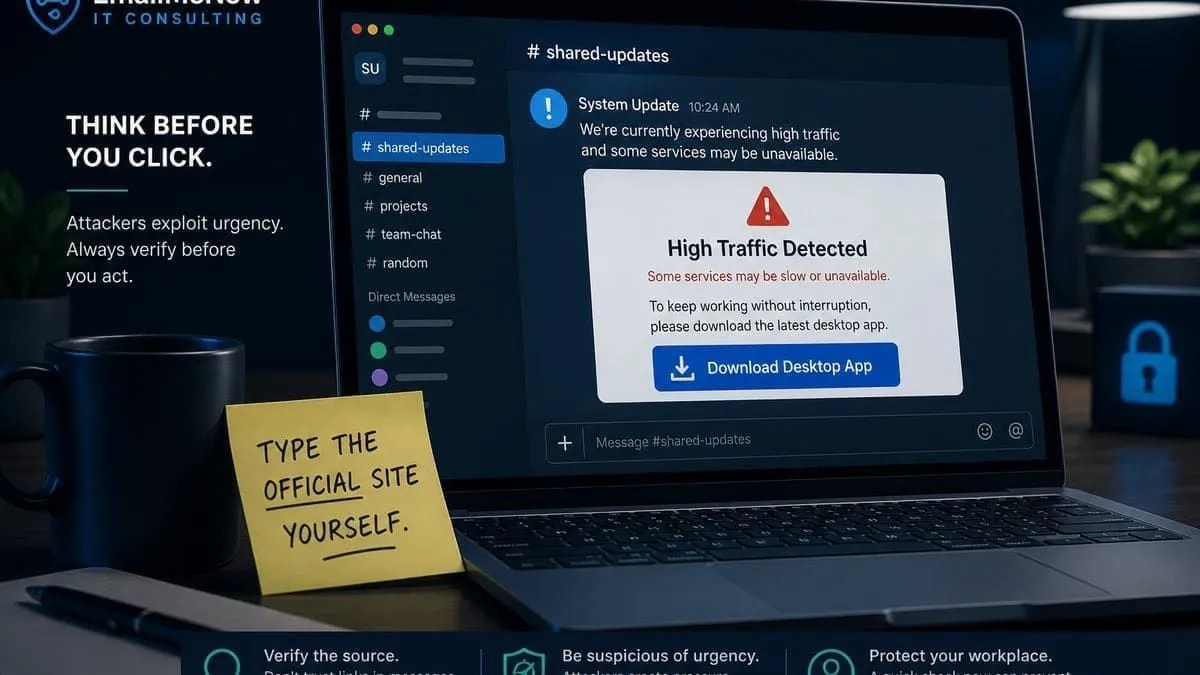
Scammers abuse real ChatGPT share links with fake high-traffic notices. OpenAI is not reported hacked. Audits (ideal 100%): pushsecurity.com 74%, microsoft.com 71%, openai.com 70%, chatgpt.com 68%.
Read Update
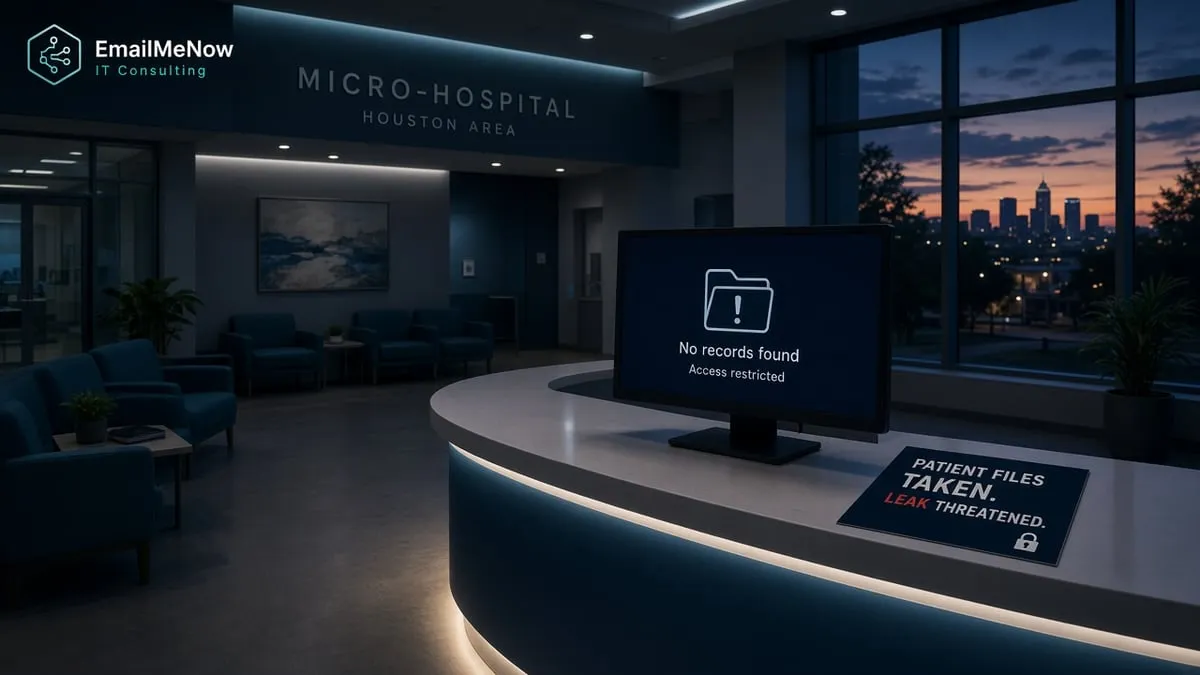
Houston-based Nutex (NUTX) filed Item 1.05 after attackers stole patient, employee, provider, and financial files. The Gentlemen claimed the listing. Audits (ideal 100%): sec.gov 88%, bayoucityhospital.com 50%, nutexhealth.com 46%, sophos.com 44%. No public YubiKey or authenticator path.
Read Update
SEC EDGAR shows 1 Form 8-K Item 1.05 material cybersecurity disclosure filed September 1, 2026. Park Dental Partners, Inc. is among the filers.
Read Update
ATF confirmed a major incident on a standalone system holding investigation-target data. Qilin listed the bureau without samples; ATF has not attributed the actor. Audits (ideal 100%): atf.gov 66%, justice.gov 66%, login.gov 63%, eforms.atf.gov 43%. eForms MFA: password + PIN, no YubiKey.
Read Update
Multi-source breach data week of August 30, 2026: Texas OAG, HHS OCR, SEC Form 8-K, HIBP, and state AG trackers. Texas YTD reports +8 (418 → 426). 7 companies/entities from source roundups.
Read Update
Leighton’s in Montrose absorbed 30–45 tap-to-pay chargebacks after stolen cards were loaded onto phones. Audits (ideal 100%): apple.com 69%, intezer.com 63%, toasttab.com 42%, leightonshtx.com 33%. Toast Web: Google Authenticator yes, YubiKey not documented.
Read Update
City of Norcross confirmed ransomware on Aug 1, 2026; public notice came late August. Data exposure, actor, and ransom still undisclosed. Audits (ideal 100%): norcrossga.net 60%, gwinnettcounty.com 57%, civicplus.com 43%. CivicPlus: Google Authenticator yes, YubiKey not documented.
Read Update
AG Dave Sunday warned Aug 28 that a MyChart Medicare Kit does not exist. Officials describe impersonation, not a MyChart platform hack. Audits (ideal 100%): attorneygeneral.gov 78%, epic.com 69%, pennmedicine.org 58%, mychart.org 54%. Epic MFA: authenticator yes, YubiKey not named.
Read Update
September 2026 Texas bar associations cyber briefing: peer incidents, domain-audit takeaways (ideal 100%), MFA notes, one IT security tip, and free member self-check links. Published on the last Sunday of the prior month.
Read Update
September 2026 Texas chambers cyber briefing: peer incidents, domain-audit takeaways (ideal 100%), MFA notes, one IT security tip, and free member self-check links. Published on the last Sunday of the prior month.
Read Update
September 2026 Texas credit unions cyber briefing: peer incidents, domain-audit takeaways (ideal 100%), MFA notes, one IT security tip, and free member self-check links. Published on the last Sunday of the prior month.
Read Update
Texas OAG published 6 new data security breach reports on August 28, 2026, affecting 7,750 Texans. Lovejoy Independent School District led the batch with 2,666 affected.
Read Update
Fortra FIRE reports a 40% Q2 2026 surge in Chameleon SEO poisoning — cloaked fake bank login pages that rank in Google and Bing but play dead to scanners. Audits (ideal 100%): texascapitalbank.com 85%, chase.com 79%, fortra.com 64%, bankofamerica.com 53% — 0/11 at 100%. Bank of America documents YubiKey; none advertise Google Authenticator.
Read Update
DOJ and FBI seized domains hard-coded into China-nexus QScan and QTRouter platforms used against NASA, the Federal Reserve, DOJ, and the U.S. Senate. Audits (ideal 100%): nih.gov 78%, energy.gov 73%, nsa.gov 55% — 0/11 at 100%. Login.gov documents YubiKey and authenticator apps.
Read Update
HHS OCR listed 3 large HIPAA breach submissions dated August 25, 2026, affecting 5,154 individuals nationally. Desert Pulmonary & Sleep Consultants, P.L.C. led the batch with 3,000 individuals.
Read Update
Have I Been Pwned added 1 breach on August 25, 2026, exposing 12,933,413 accounts globally. Carhartt led the batch with 12,933,413 accounts.
Read Update
Heights Finance confirmed a May 2026 third-party cloud incident. Texas OAG lists 734,828 Texans. Audits (ideal 100%): heightsfinance.com 60%. MyAccount login is cell-phone only — no YubiKey or Google Authenticator.
Read Update
Microsoft Defender ShieldBreak (CVE-2026-69414) is still unpatched. Apple fixed ImageIO CVE-2026-65346 in iOS 26.6.1. Audits (ideal 100%): microsoft.com 71%, apple.com 69%. Microsoft and Apple Accounts document YubiKey; Apple does not document Google Authenticator.
Read Update
U.S. Bank is investigating a LockBit leak-site claim. The bank says a fourth-party event outside its environment; no evidence its systems were hit. Audits (ideal 100%): usbank.com 68%. MFA: Fail (SMS OTP; no YubiKey/TOTP).
Read Update
Multi-source breach data week of August 23, 2026: Texas OAG, HHS OCR, SEC Form 8-K, HIBP, and state AG trackers. Texas YTD reports +14 (404 → 418). 18 companies/entities from source roundups.
Read Update
Beazley Security’s Q2 2026 threat report: disclosed CVEs +36%, CISA KEV +10%, but 67% of ransomware still starts with stolen VPN/RDP passwords. Device-code phishing beats MFA. Audits (ideal 100%): hackerone.com 88%, nist.gov 84%, beazley.security 78% — none at 100%.
Read Update
Have I Been Pwned added 1 breach on August 22, 2026, exposing 568,972 accounts globally. Golf Canada led the batch with 568,972 accounts.
Read Update
UT San Antonio detected attempted unauthorized activity at the network edge, took systems offline, and delayed fall classes to Aug 24. No evidence of data theft. Audits (ideal 100%): utsa.edu 70%, passphrase.utsa.edu 34%. Duo recommends YubiKey; Google Authenticator not documented.
Read Update
California's data breach list added 4 notices on August 21, 2026. California does not publish residents-affected counts — this roundup tracks reporting visibility.
Read UpdateSB 2610 may help limit exemplary damages for eligible businesses that maintain a documented cybersecurity program; not legal advice or a guarantee.